Cybersecurity – systems for hotels
CYBERSECURITY
Merizon delivers comprehensive cybersecurity solutions based on a thorough audit, current criteria and the latest amendments to legislation.
What should a hotel keep in mind?
- The amended Act on the National Cybersecurity System (UKSC), implementing NIS2 (Network and Information Security Directive 2), was signed by the President in February 2026. Large businesses are now required to self-identify: they must assess on their own whether they meet the criteria and register with the competent register.
- PCI DSS 4.0 Compliance (Payment Card Industry Data Security Standard)
- CDE Network Segmentation: the cardholder data environment (CDE – e.g. POS terminals, the PMS server) should be fully isolated from the guest network and the general office network.
- Network Isolation: the guest network should be isolated from the administrative network.
- Vulnerability scanning: the hotel should run internal network vulnerability scans every 3 months and external scans performed by a certified ASV (Approved Scanning Vendor).
- Personal data – the GDPR requires the hotel to apply "appropriate technical measures" to prevent data leaks.
- According to the case law of the Court of Justice of the EU, IP addresses may constitute personal data if the controller has the legal and technical means (e.g. the PMS booking system database) to identify the individual using a given IP address at a given time.
- Security breach alerting/reporting: a data breach must be reported by the hotel to the Polish Data Protection Authority (UODO) within 72 hours and to CSIRT NASK within 24 hours.
- Logs Retention: storing (encrypted) logs for up to 12 months. Telecommunications law requires operators to collect and retain data on the use of telecommunications services.
- Firewalls (Change Logs): keeping logs of who changed the firewall rules and when.
- Patch Management: regular software updates for routers, switches and operating systems, within 30 days of release.
- Active monitoring & Alerting – NOC (Network Operations Center), 24/7: detecting unusual network behaviour that may indicate a ransomware infection or an attempt to steal a database; the NOC monitors firewalls and switches.
- Reporting: monthly reports (blocked attacks, intrusion attempts, connection attempts from suspicious IP addresses).
- Documentation: storing documentation in a secured cloud (MFA – Multi-Factor Authentication).
- Access Authentication: MFA is mandatory for all administrative access to the hotel network (a password alone is not enough). An IT company logging in to the firewall remotely must use MFA.
- Unique Identification: shared accounts (e.g. "service", "admin") are prohibited. Every employee must log in with a personal account, so it is clear who made changes.
- Back-ups: regular backups (of switch and firewall configurations).
- Password management: changing access passwords to active network equipment.
- Maintenance: equipment servicing.
- Updating: reviewing firewall rules (at least every 6 months for relevance and security).
- Troubleshooting: incident response in line with the SLA.
- Minimum necessary: restricting access as far as possible, e.g. to firewalls; granting "read only" permissions.
- Time synchronization: all devices (servers, firewalls) must have synchronised time (NTP), so the exact sequence of events can be established after a breach.
- Hardening: network devices must not use default manufacturer passwords (e.g. "admin/admin"). Each device must be configured according to secure baselines.
- Cybersecurity trainings
- Firewalls Redundancy – recommended
Selected projects
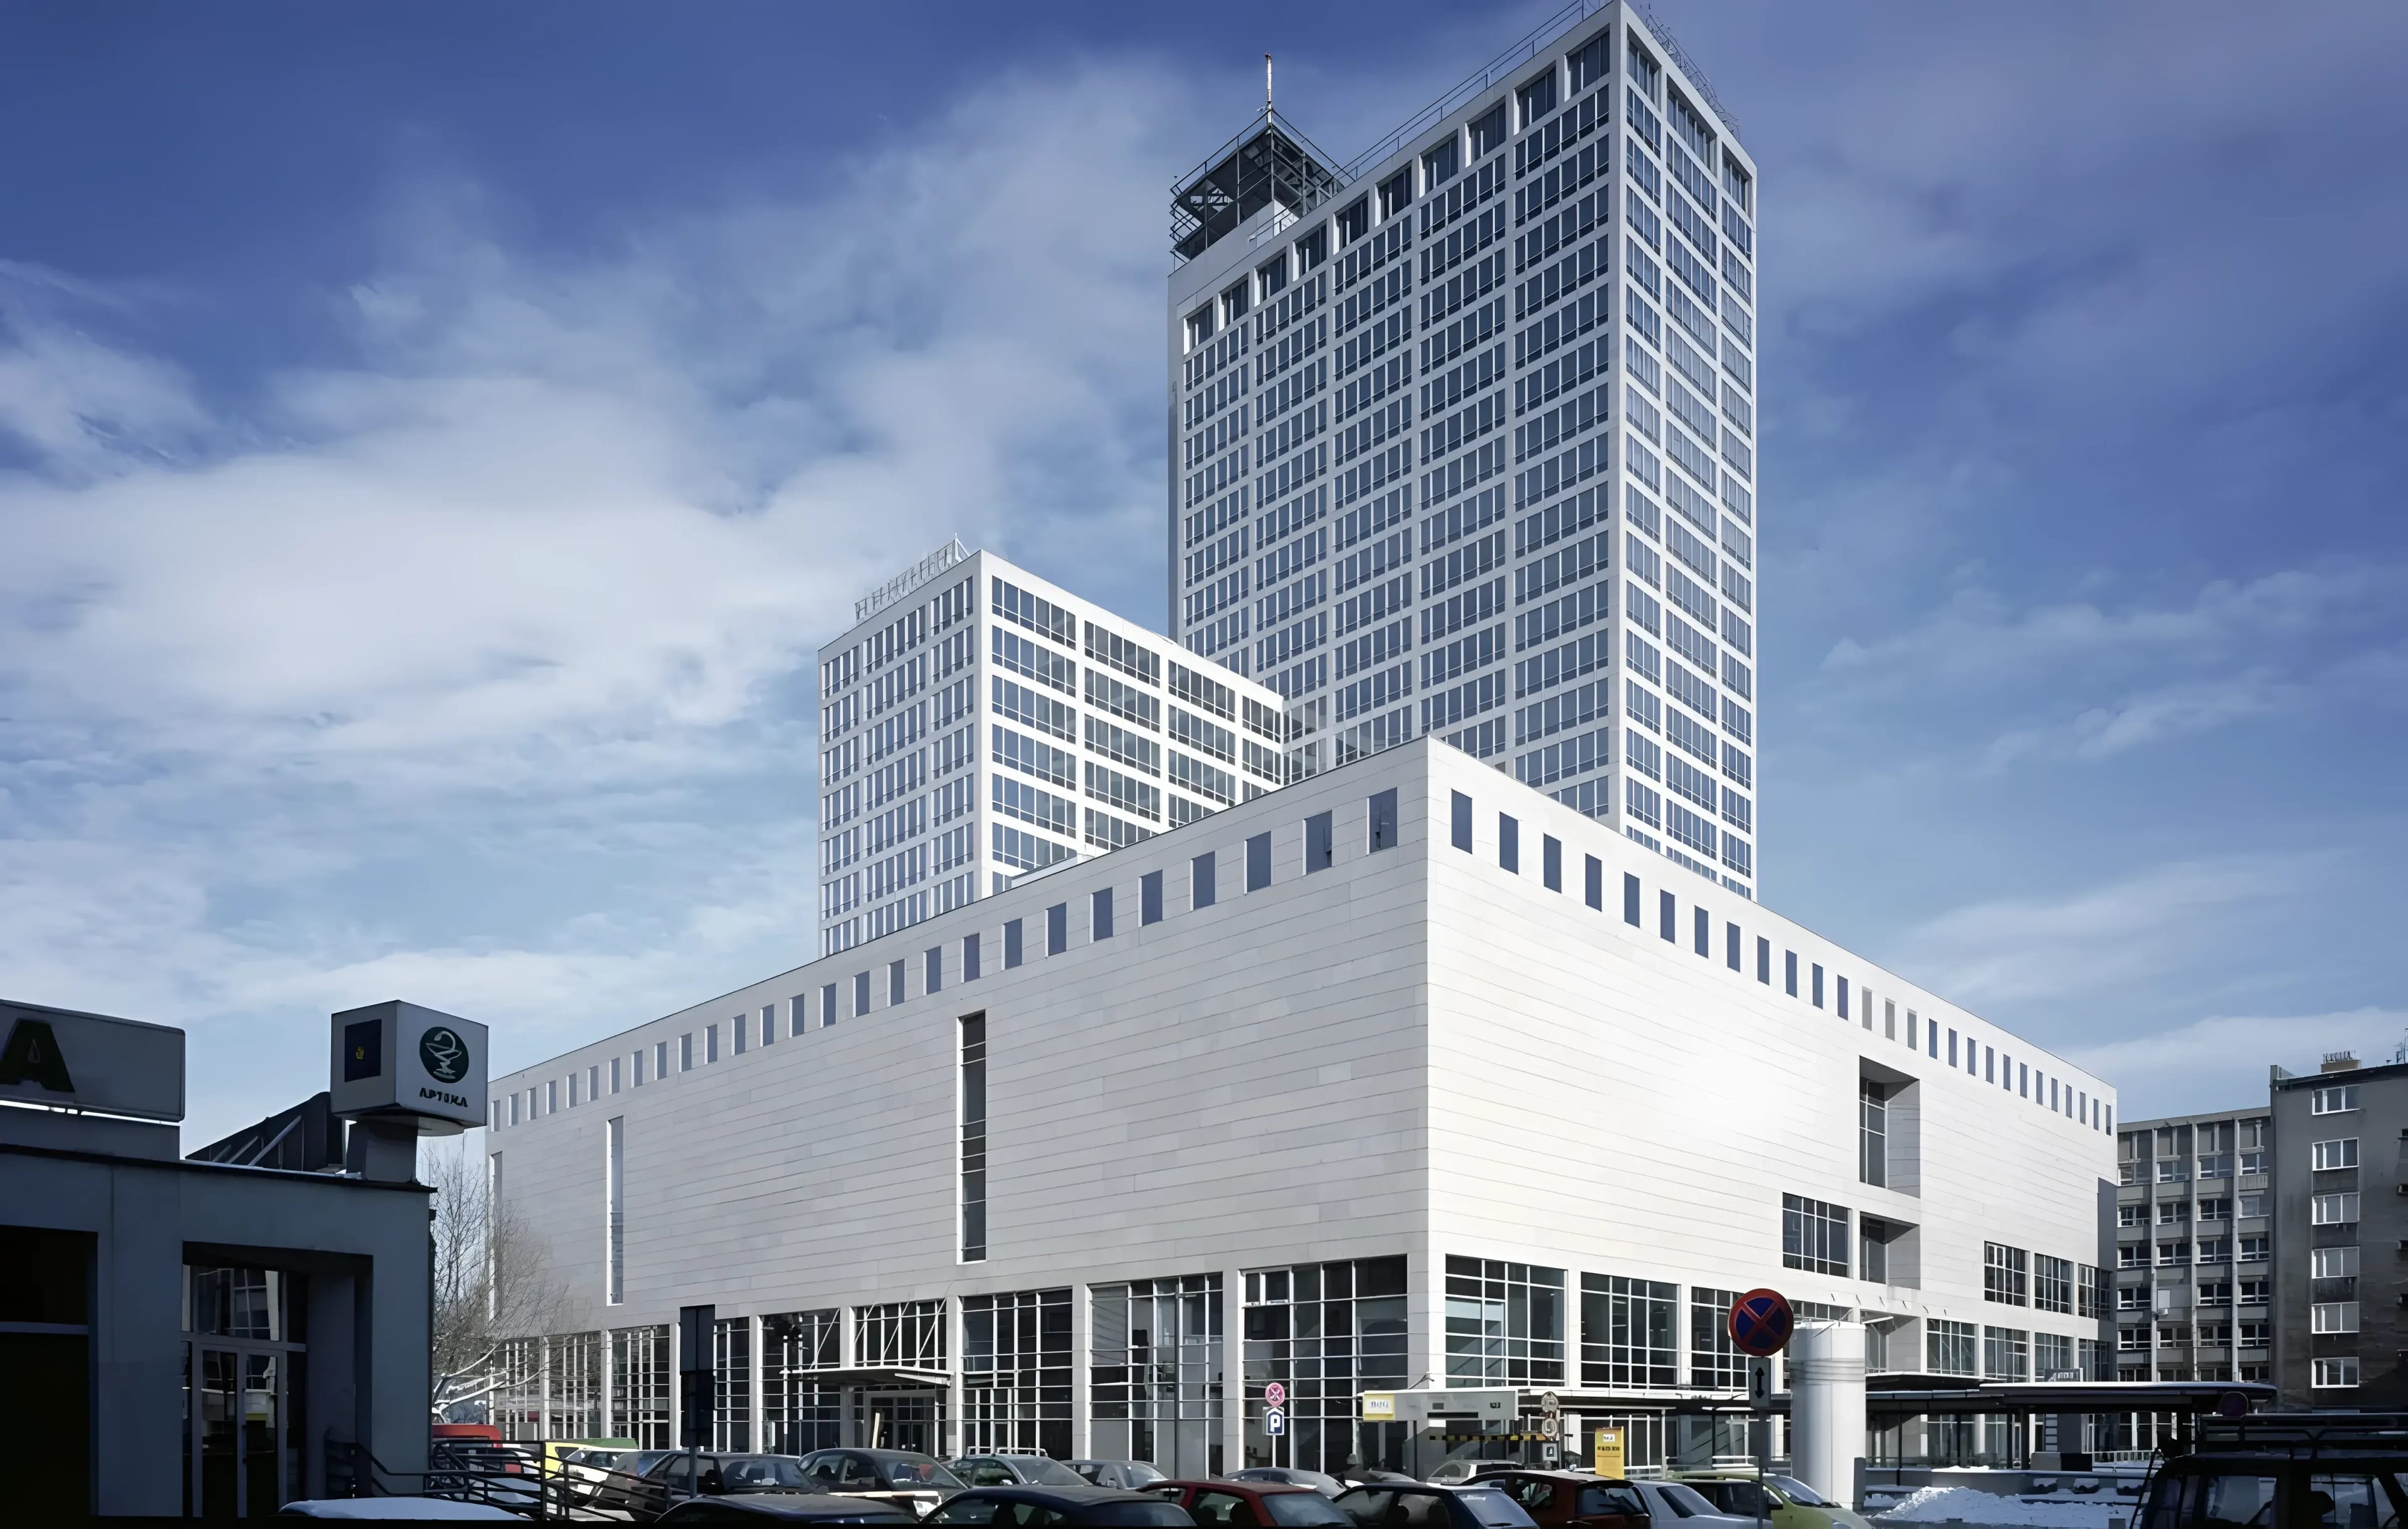
 Katowice
December 2017Courtyard by Marriott KatowiceKatowice, Poland
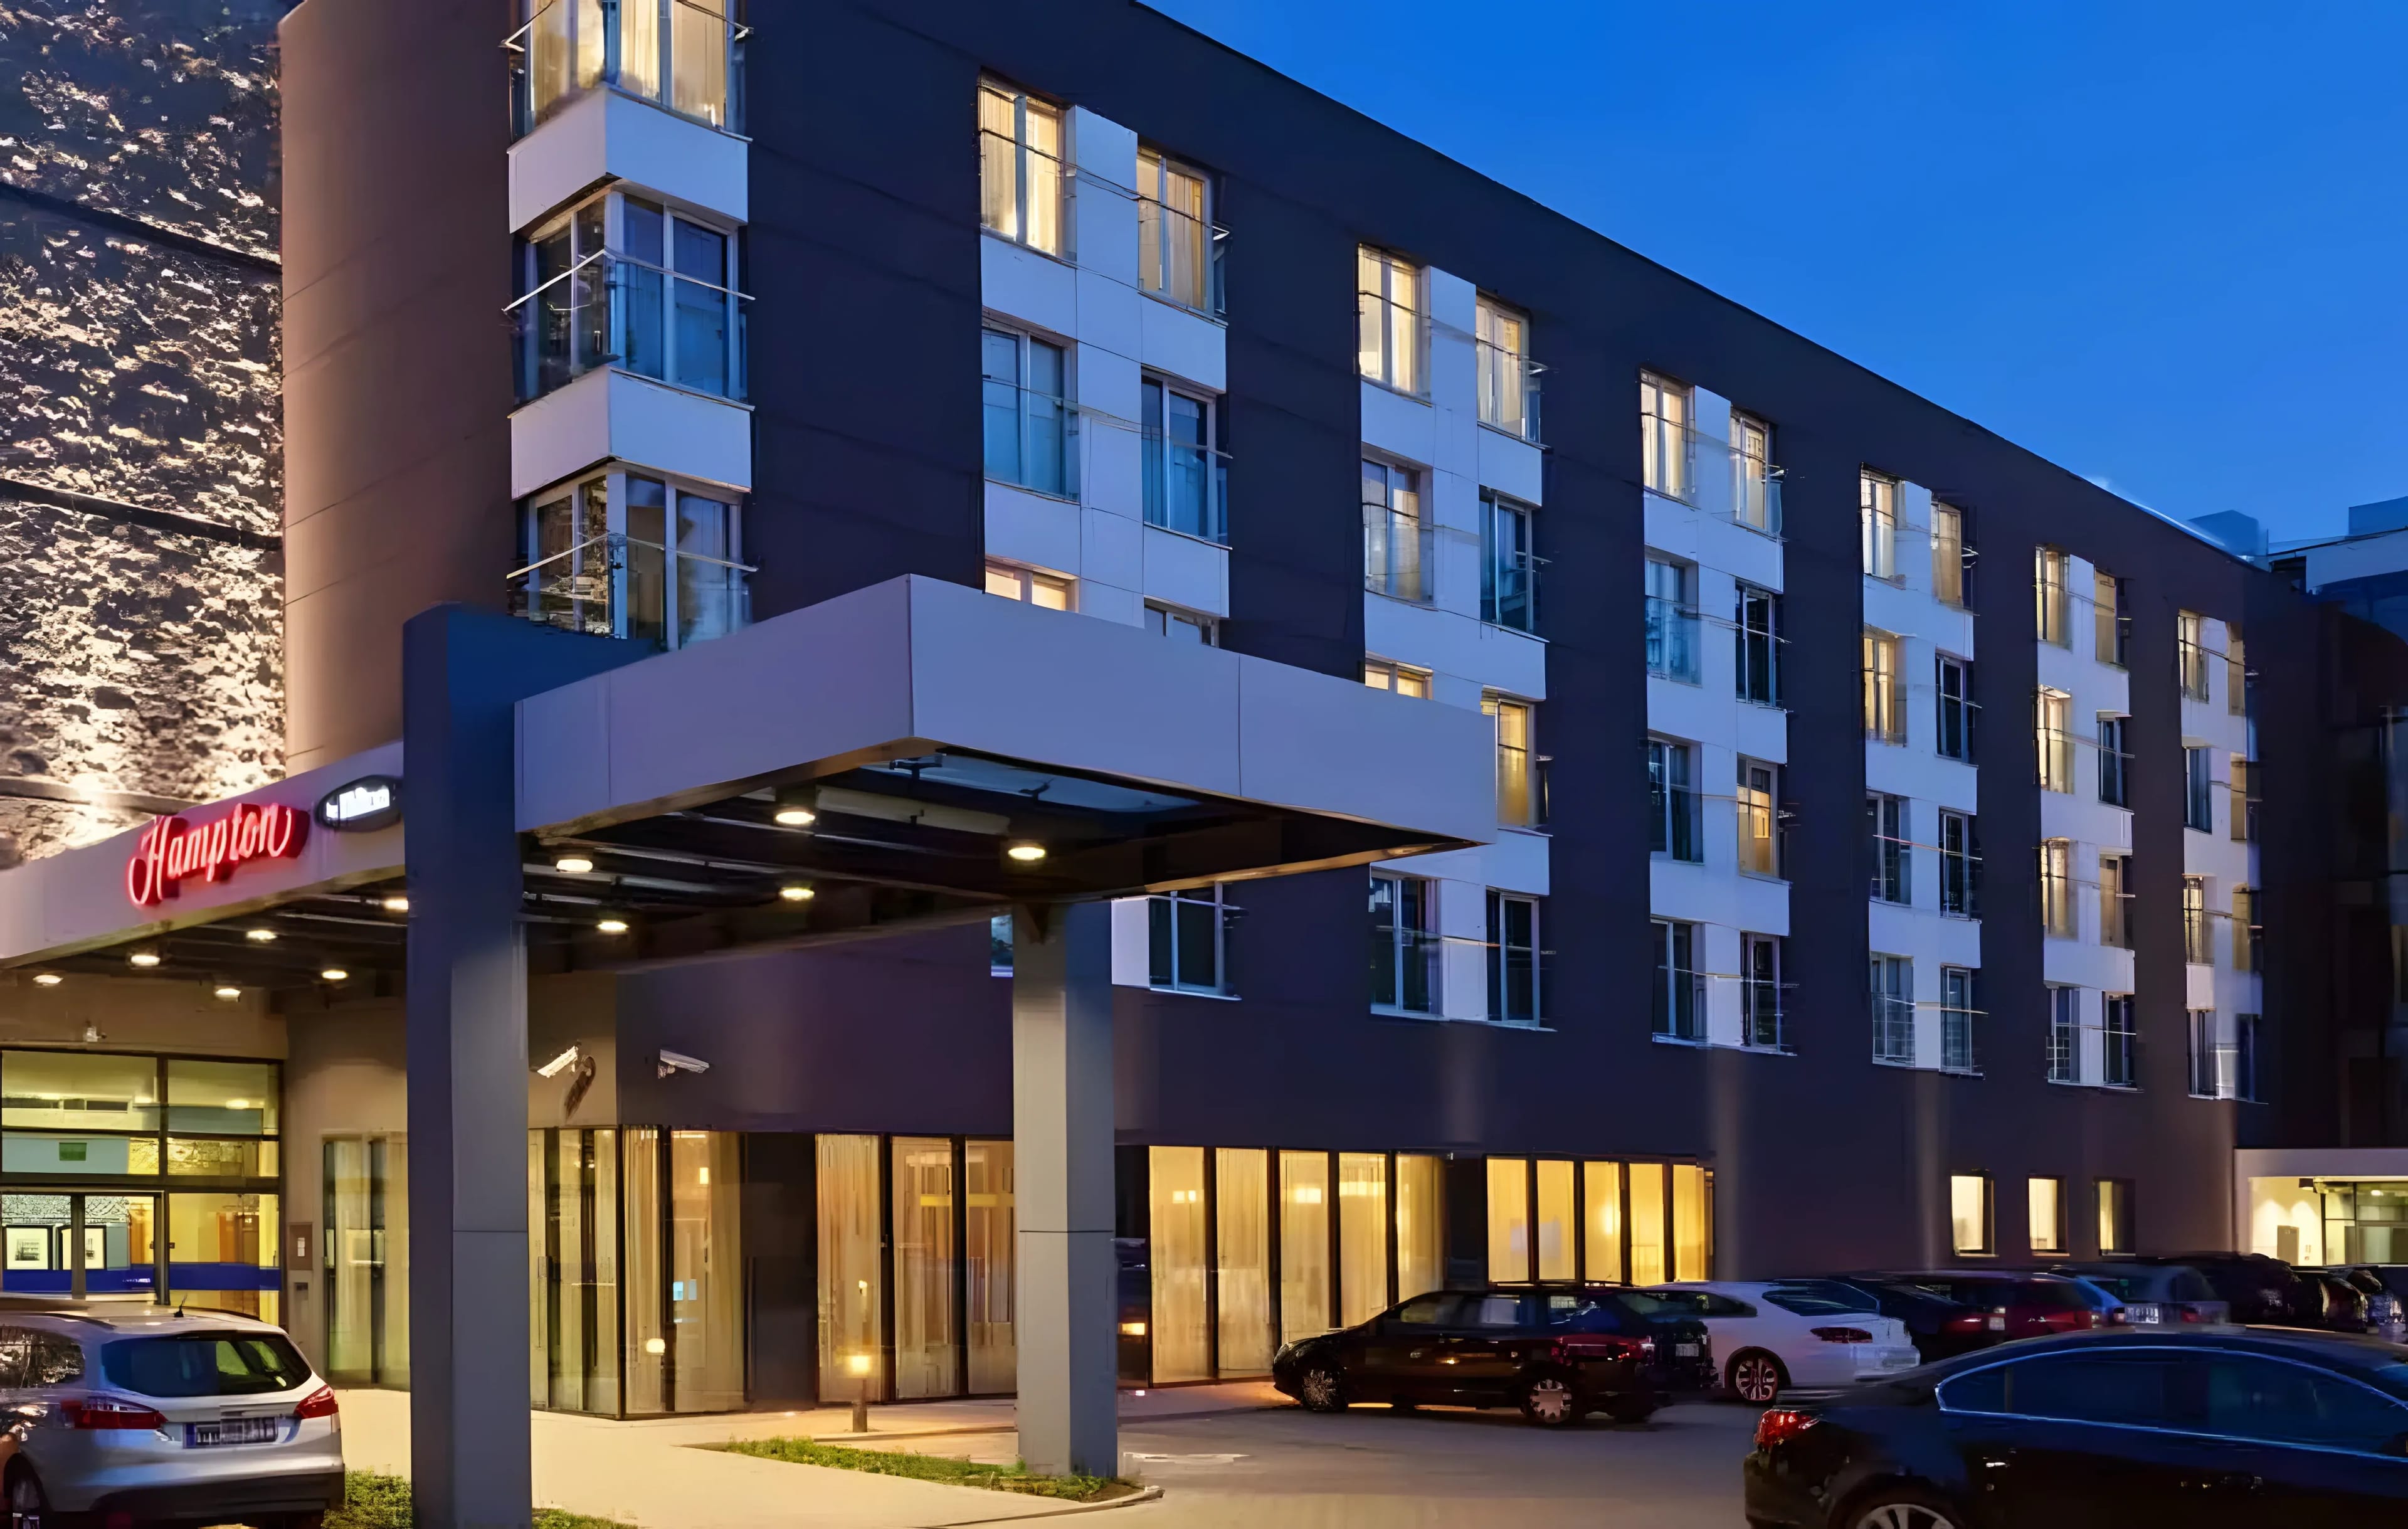
 Warsaw
December 2017Hampton by Hilton Warszawa AirportWarsaw, Poland
 Warsaw
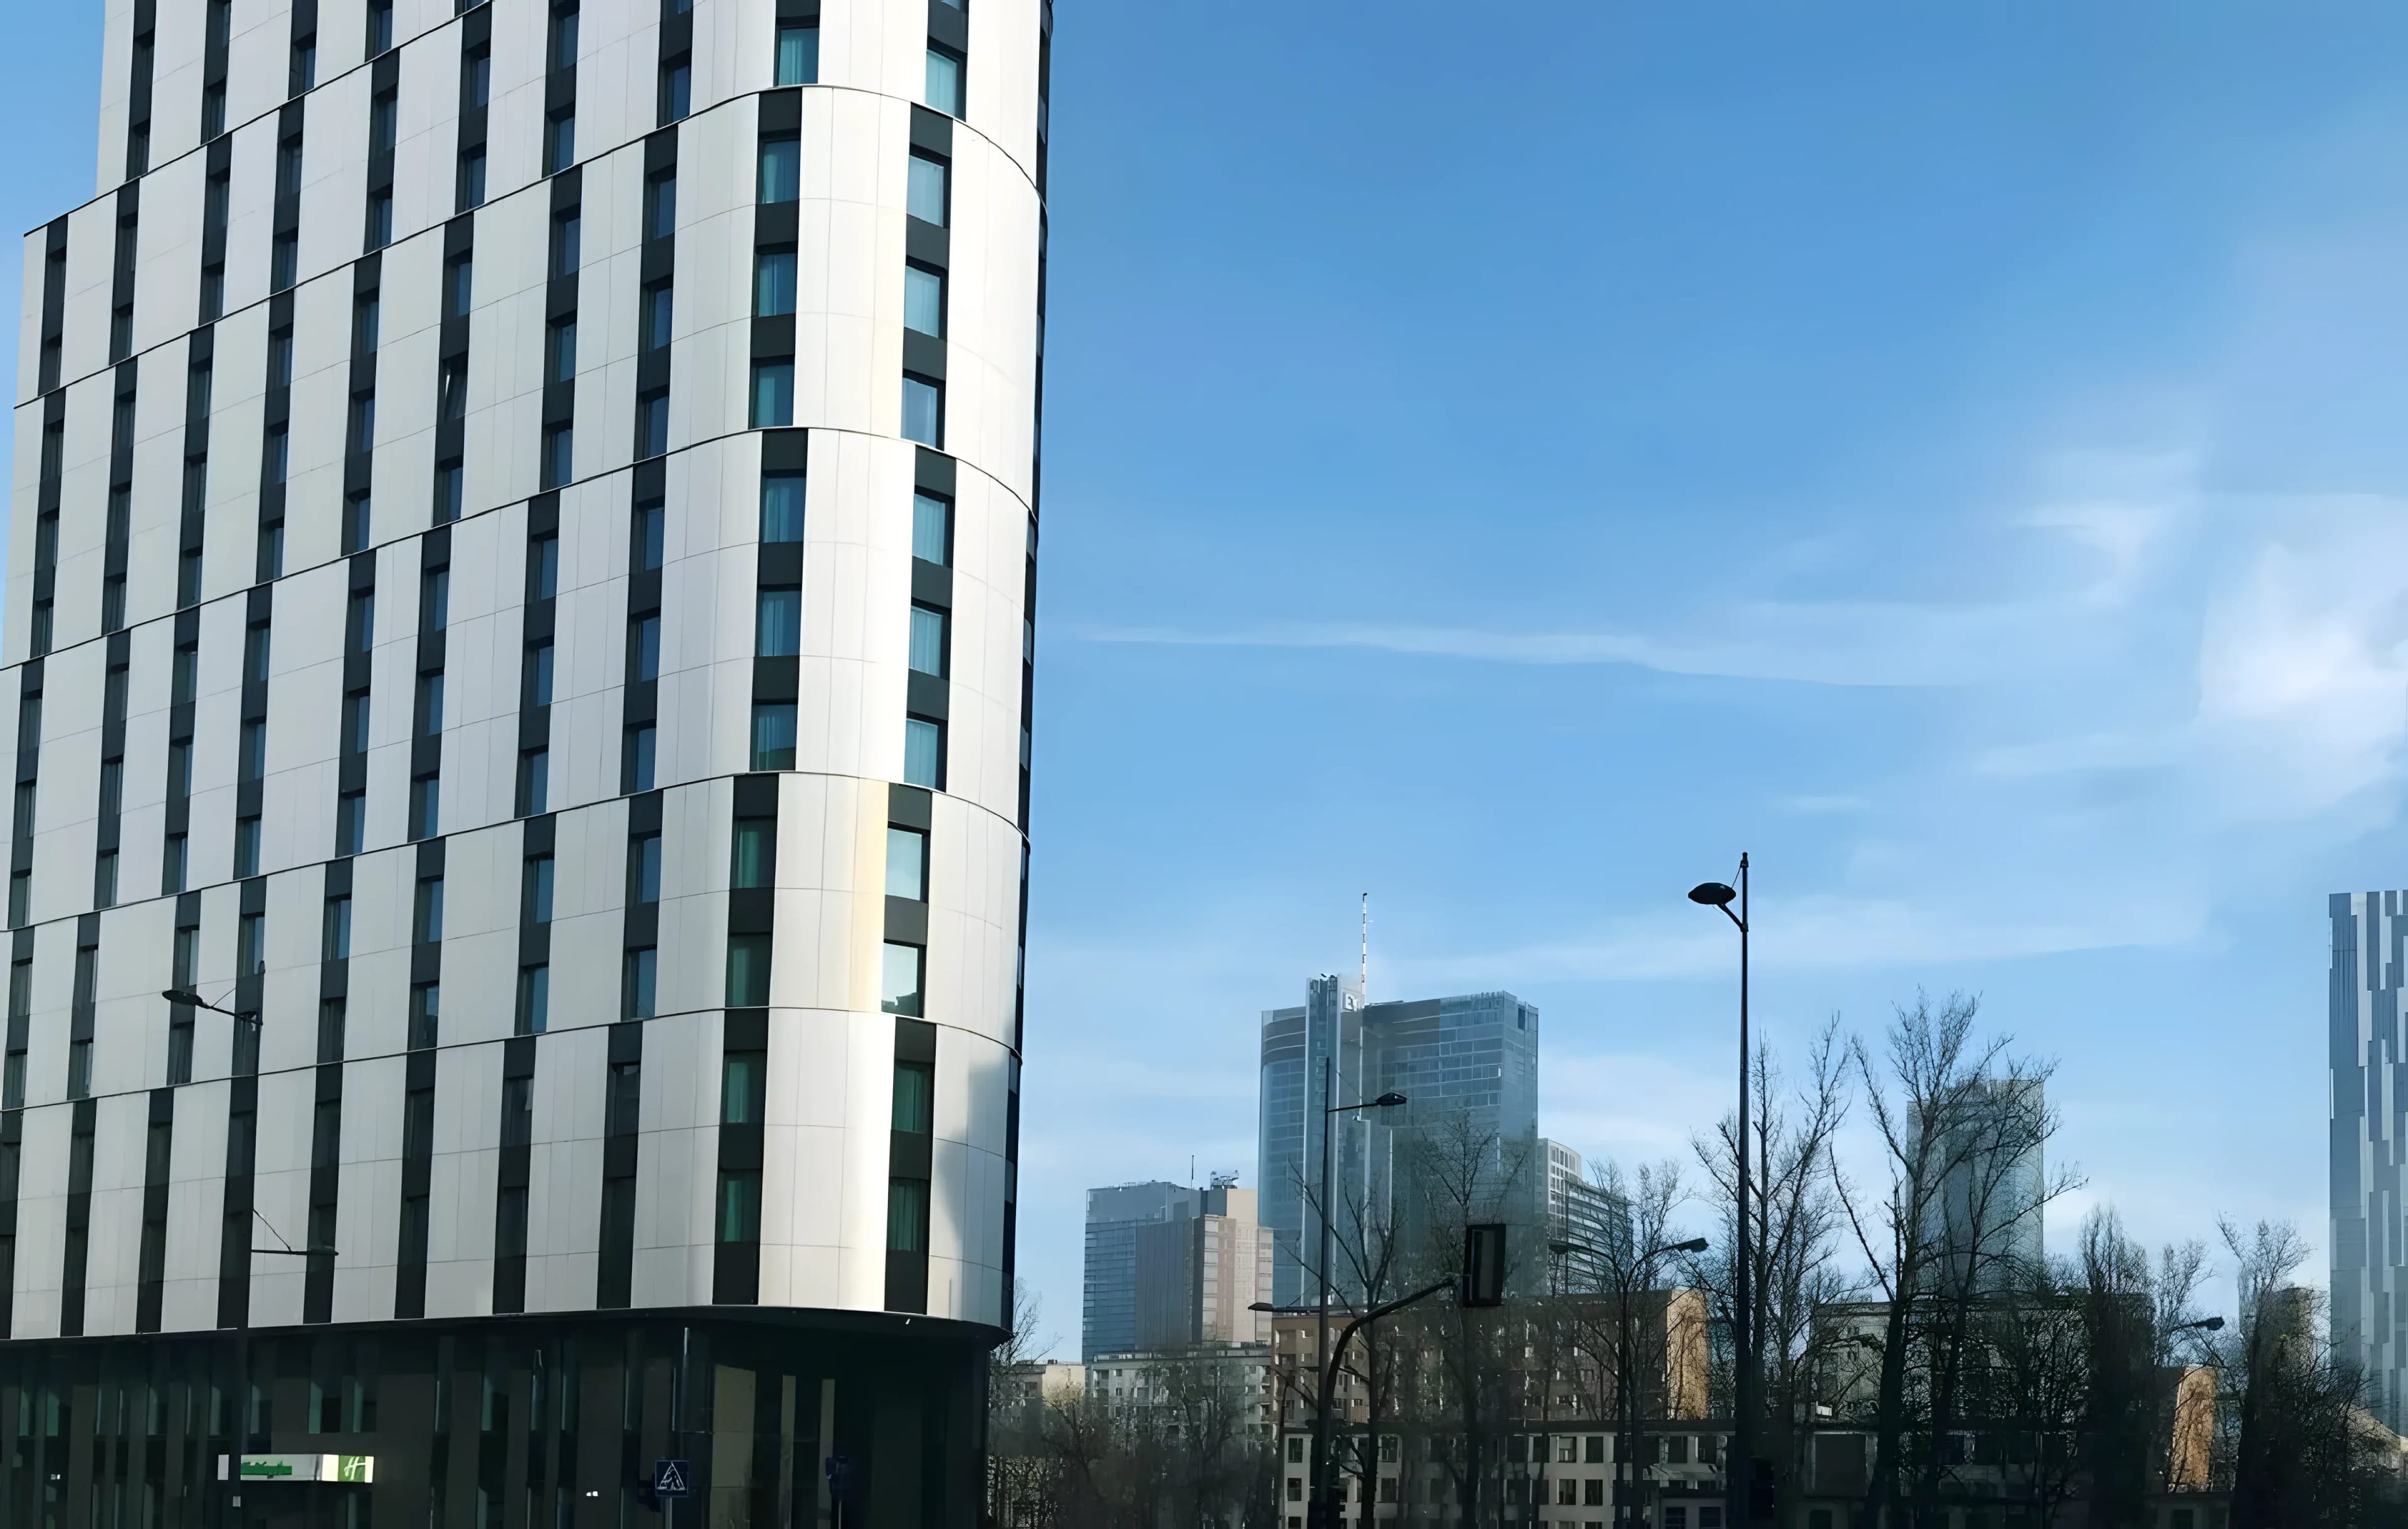
December 2017Holiday Inn WarszawaWarsaw, Poland
Customized solutions prepared on basis of specific needs of our customers. Contact us. See how we may be of help to you.